- Security
- Website
- Maintenance
Basic Website Security Checklist for Businesses
A practical website security checklist every business should apply: HTTPS, updates, strong authentication, backups, input validation and more.
3 min read
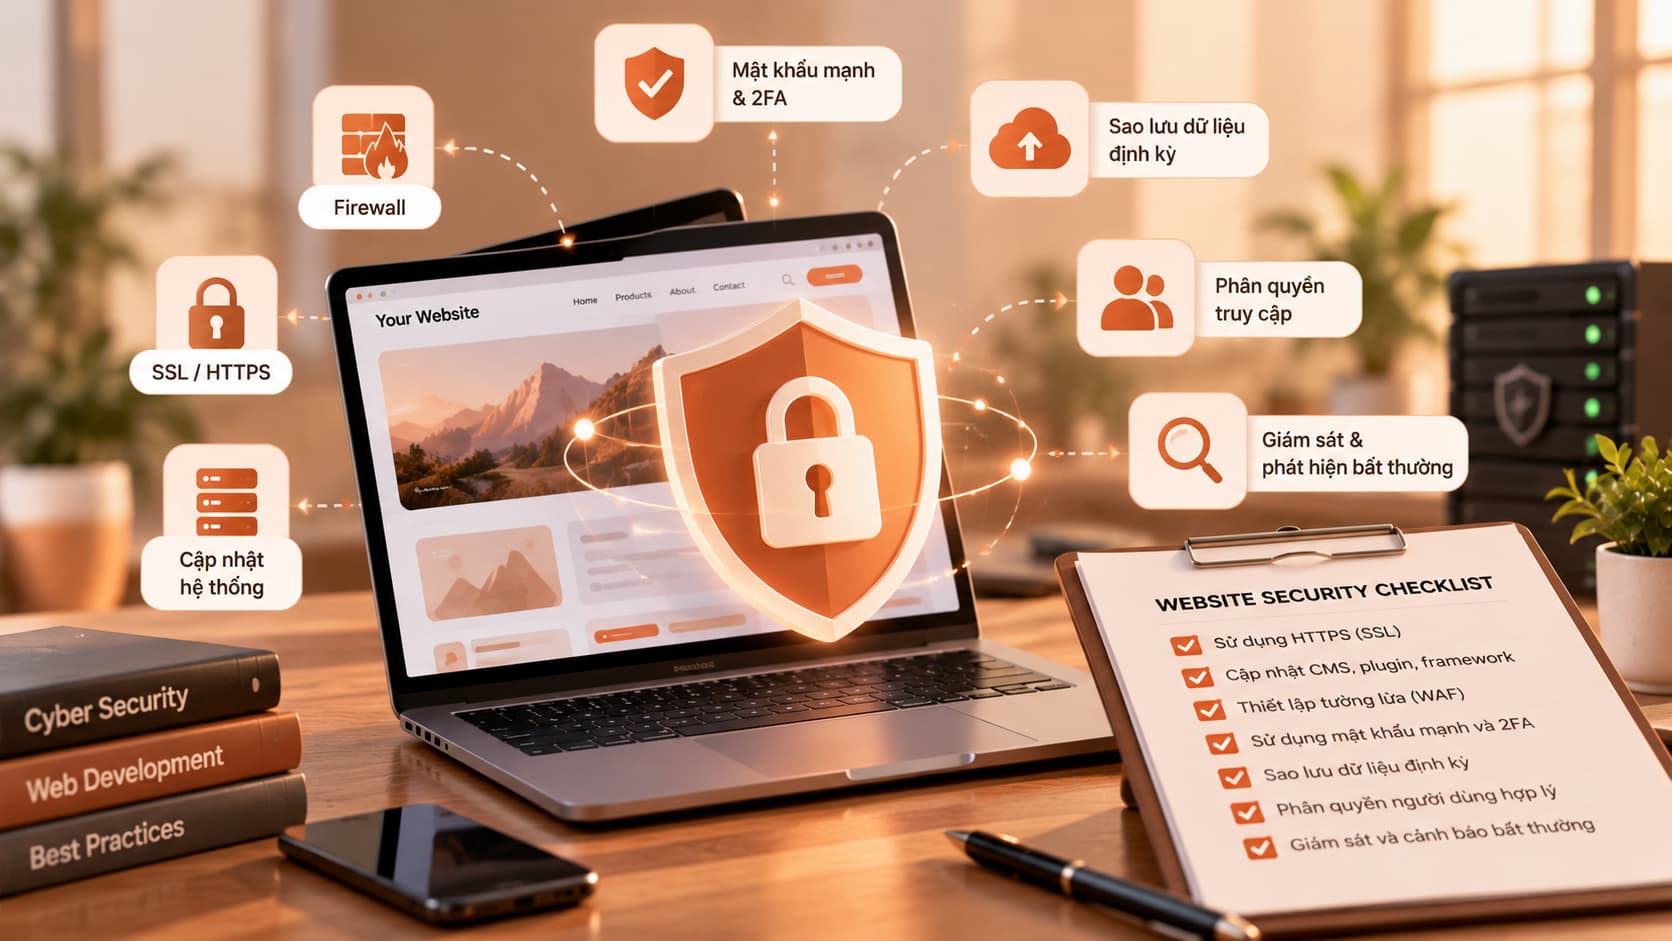
Website security is not only a concern for large companies. A small business website can still be hit by automated attacks that inject malware, send spam, steal customer data or disrupt operations. The good news is that most common risks can be reduced significantly with a handful of basic measures. Use this website security checklist to review your own site.
Why website security matters for businesses
A website often holds contact details, orders, admin accounts and sometimes customers' personal data. A breach costs more than the clean-up: it can damage your brand, trigger browser or search engine warnings, and create legal obligations around personal data protection. Prevention is always cheaper than incident response.
The basic website security checklist
1. Infrastructure and connections
- ✅ Serve the whole site over HTTPS, redirect HTTP automatically and renew certificates automatically.
- ✅ Enable basic security headers: Strict-Transport-Security, Content-Security-Policy, X-Content-Type-Options, Referrer-Policy and frame-ancestors to prevent clickjacking.
- ✅ Do not leak unnecessary information: disable directory listing and hide detailed error messages in production.
2. Software updates
- ✅ Regularly update the operating system, web server, CMS, framework, plugins and libraries.
- ✅ Remove plugins, themes, accounts and services you no longer use.
- ✅ Watch vulnerability alerts for your dependencies (for example npm audit or Dependabot).
3. Authentication and access control
- ✅ Require strong passwords and never reuse passwords across systems.
- ✅ Enable two-factor authentication (2FA) for admin, hosting, domain and email accounts.
- ✅ Apply the principle of least privilege: every person and service gets only the access it needs; the application's database user should not be root.
- ✅ Revoke access immediately when staff leave or a partner engagement ends.
4. Data and code
- ✅ Validate input on the server, not only in the browser.
- ✅ Use parameterized queries against SQL injection; escape output to prevent XSS.
- ✅ Check the type and size of uploaded files and never allow executables to run from the upload folder.
- ✅ Never store plain-text passwords: use a dedicated hashing function such as bcrypt or Argon2.
- ✅ Keep secrets and passwords out of source code and Git repositories.
5. Abuse prevention
- ✅ Apply rate limiting to login, password reset, contact forms and APIs.
- ✅ Protect public forms against spam (honeypot fields, CAPTCHA when needed).
6. Backup and recovery
- ✅ Back up the database and files regularly, keeping at least one copy separate from the main server.
- ✅ Test restoring from backups periodically; an untested backup may not work when you need it.
- ✅ Log logins and important actions, and make sure someone reviews anomalies.
Understanding the OWASP Top 10
The OWASP Top 10 is a list of the most common categories of web application security risks, compiled and periodically updated by the OWASP community. It covers issues such as broken access control, cryptographic failures, injection, security misconfiguration and vulnerable components. Developers and project managers should know it so security requirements are set from the start. You can read it at OWASP Top 10.
Conclusion
No website is perfectly secure, but a basic website security checklist applied consistently removes most of the easily exploited weaknesses. Treat security as ongoing maintenance rather than a one-off task. If you want your business website's security reviewed or upgraded, get in touch with us.